Ecommerce Website Security Best Practices: How to Protect Your Online Store
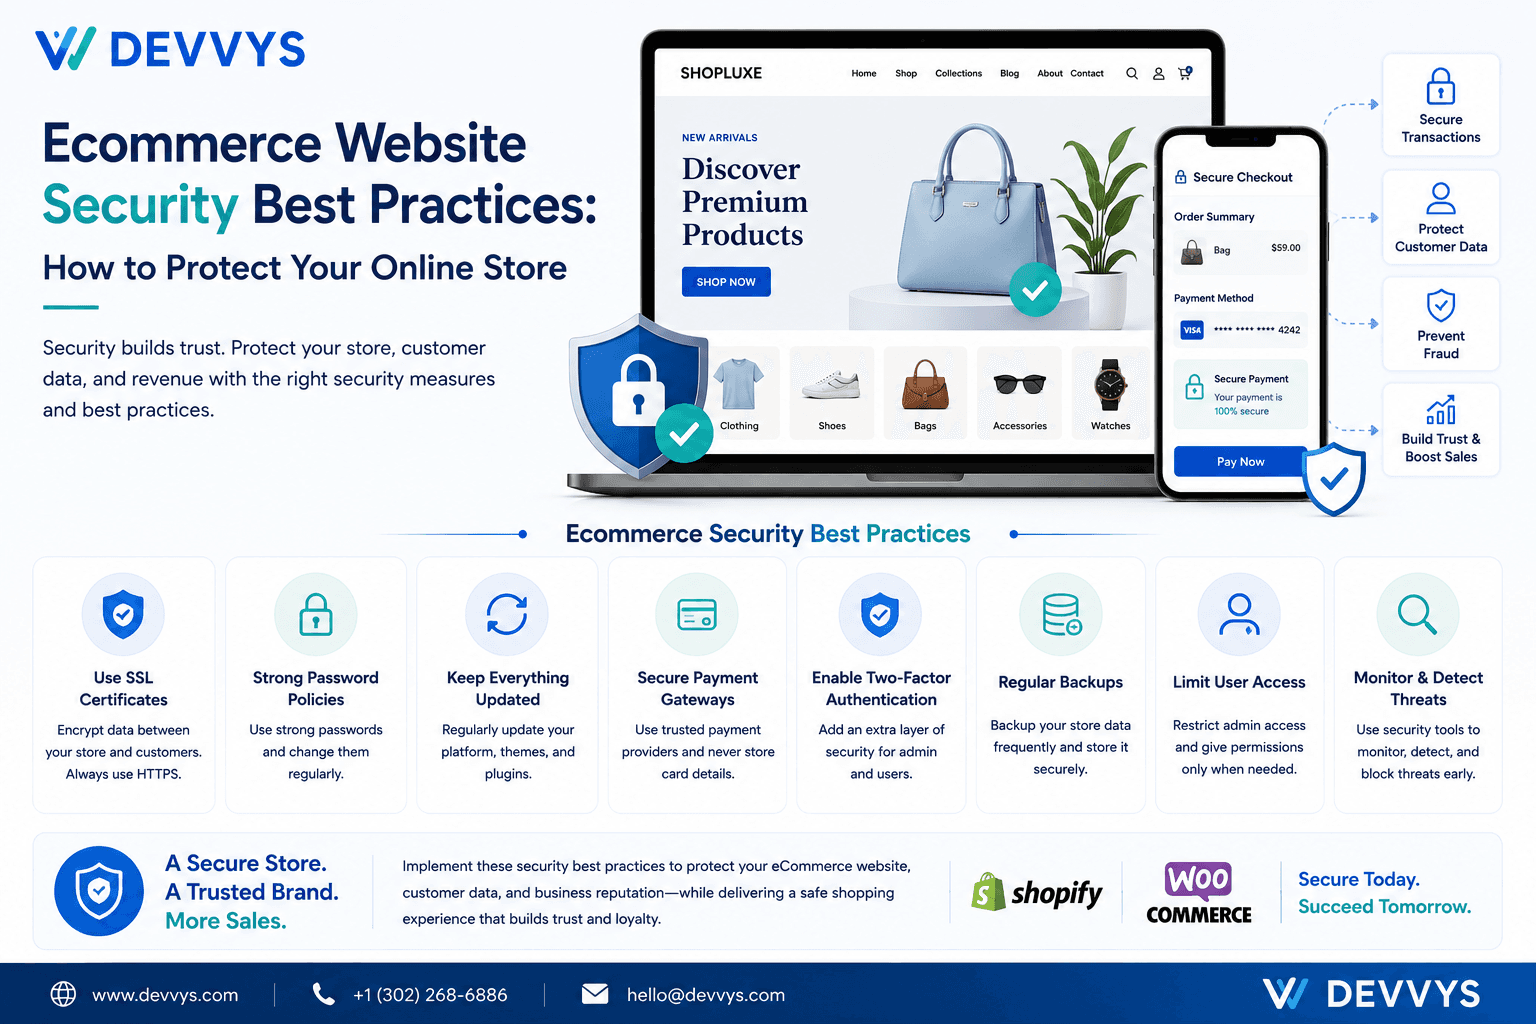
Ecommerce security is one of the most important parts of running an online store. When customers share personal details, payment information, and login credentials, they expect the business to protect that information. That is why following E-commerce Website Security Best Practices is essential for any store that wants to build trust and avoid costly problems.
A secure ecommerce website protects both the business and the customer. It helps reduce fraud, prevents unauthorized access, and lowers the risk of data breaches. It also supports long-term brand trust because customers are more likely to buy from a store they feel confident using.
This article explains the key security practices every ecommerce business should follow. Whether you are launching a new store or improving an existing one, these steps can help make your website safer and more reliable.
Use HTTPS and SSL
One of the most basic but important security steps is using HTTPS and SSL encryption. This helps protect data as it moves between the customer’s browser and your website.
Why It Matters
Without encryption, sensitive information can be intercepted more easily. HTTPS also shows customers that the site is secure.
What to Do
Install an SSL certificate.
Make sure the entire site uses HTTPS.
Redirect all non-secure pages to the secure version.
Keep Software Updated
Outdated software is one of the most common security risks in ecommerce. Themes, plugins, apps, and platform files should always be kept up to date.
Why It Matters
Updates often fix security vulnerabilities that hackers may try to exploit.
What to Do
Update your ecommerce platform regularly.
Keep plugins and apps current.
Remove tools you no longer use.
Use Strong Passwords and Access Controls
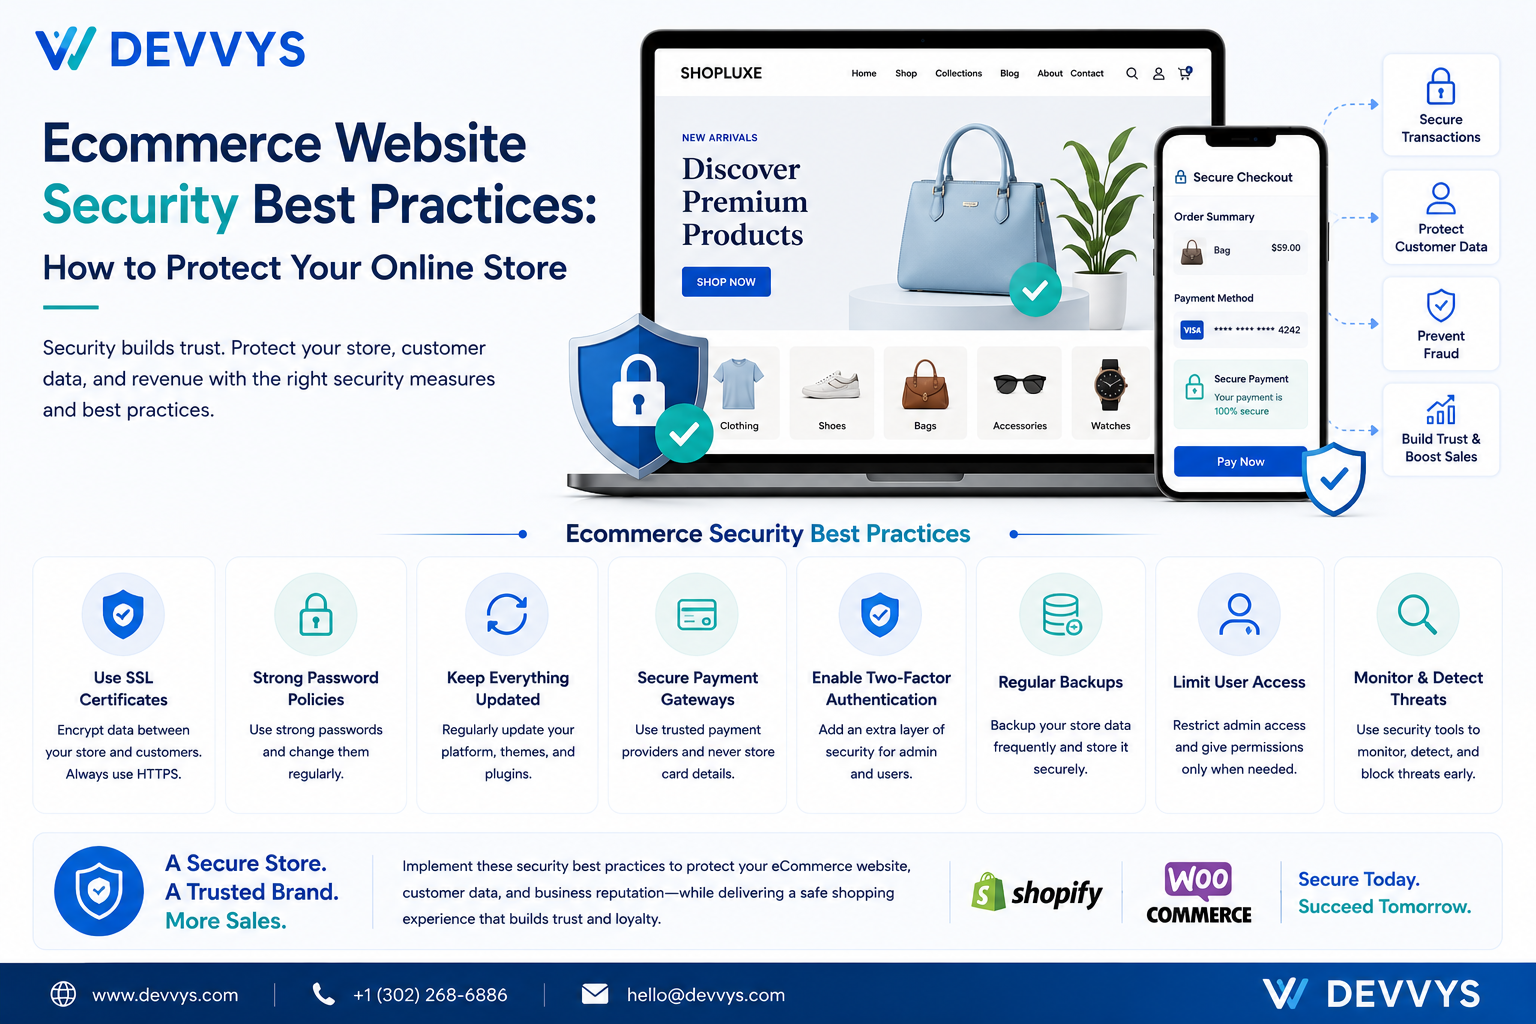
Weak passwords make it easier for attackers to gain access to admin accounts. Access should be limited to the people who truly need it.
Why It Matters
The fewer people who have admin access, the lower the risk of accidental or unauthorized changes.
What to Do
Use strong, unique passwords.
Enable two-factor authentication.
Limit staff permissions based on role.
Secure Customer Data
Customer information should be protected at every stage. This includes names, addresses, email addresses, and payment details.
Why It Matters
A data leak can damage trust and lead to legal and financial problems.
What to Do
Store only the data you actually need.
Use secure payment gateways.
Follow privacy and data protection laws.
Monitor for Threats
Security is not a one-time task. Ecommerce websites should be monitored regularly for suspicious activity.
Why It Matters
Early detection can help prevent serious damage.
What to Do
Review logs and alerts.
Watch for unusual login attempts.
Use security tools and malware scans.
Final Thoughts
Following Ecommerce Website Security Best Practices is not optional. It is a core part of building a trustworthy and successful online store. By using HTTPS, keeping software updated, protecting access, securing customer data, and monitoring threats, businesses can greatly reduce their risk.
A secure website helps protect revenue, reputation, and customer confidence. In ecommerce, that security is one of the strongest foundations for long-term growth.